Site owner
You need a quick inventory of public pages that return errors or redirect unexpectedly.
Use a public starting URL, then confirm important findings in a browser.
Safety guide
The short answer is usually yes, when you use a reputable checker on public pages and understand what it can request. This guide separates ordinary crawling from genuine privacy and security risks.
Common doubts
Most worries come from treating every checker as if it had the same access, purpose, or technical behavior. These distinctions make the risk easier to judge.
A normal web-based checker requests web pages and follows links; it cannot browse local files, saved passwords, or unrelated browser data just because you entered a URL.
What to do instead
Submit a public test page and avoid installing software from an unknown publisher.
A timeout, 404 response, blocked request, or redirect usually describes availability, not an attack. Link status alone does not prove that a site has been compromised.
What to do instead
Review the response context and confirm suspicious results manually.
If a page contains an unpublished path, customer information, a preview token, or an internal hostname, submitting it may disclose that address to the service.
What to do instead
Use a public copy or remove secrets before checking.
Free access does not automatically explain retention, logging, rate limits, or whether submitted URLs are stored. The service still deserves a basic privacy review.
What to do instead
Read its policy and use non-sensitive URLs for routine checks.
How it works
A link checker is a crawler or request tool that tests destinations and reports responses. It is useful for maintenance, but it is not a full security scanner.
The checker receives a page or site address and may discover links from its public HTML, depending on its crawl rules.
It sends ordinary web requests and records signals such as status codes, redirects, timeouts, blocked access, and unreachable hosts.
You decide whether a result is genuinely broken, temporarily unavailable, intentionally restricted, or simply inaccessible to automated requests.
Related reading
The safest workflow depends on what you are checking, who controls the destination, and whether the URL carries private context.
Risk comparison
Use the left column for ordinary public-site maintenance. The right column signals when you should pause, change tools, or avoid submitting the URL.
| Routine public check | Higher-risk situation | |
|---|---|---|
| Page visibility | Public page anyone can open | Private, preview, staging, or internal page |
| URL contents | Clean URL with no secret token | Password reset, invite, session, or access token in the URL |
| Data sent | Public web addresses and page responses | Customer records, unpublished paths, or confidential documents |
| Tool source | Known service with clear ownership and policy | Unknown download, opaque extension, or unexplained installer |
| Primary purpose | Find unavailable or misdirected destinations | Detect malware, vulnerabilities, or unauthorized access |
| Result handling | Review, fix, and retest a small set of findings | Automatically trust every warning or expose the report publicly |
A safer workflow
The difference is often visible in the workflow: remove sensitive context before testing, then verify unusual results instead of treating automation as proof.
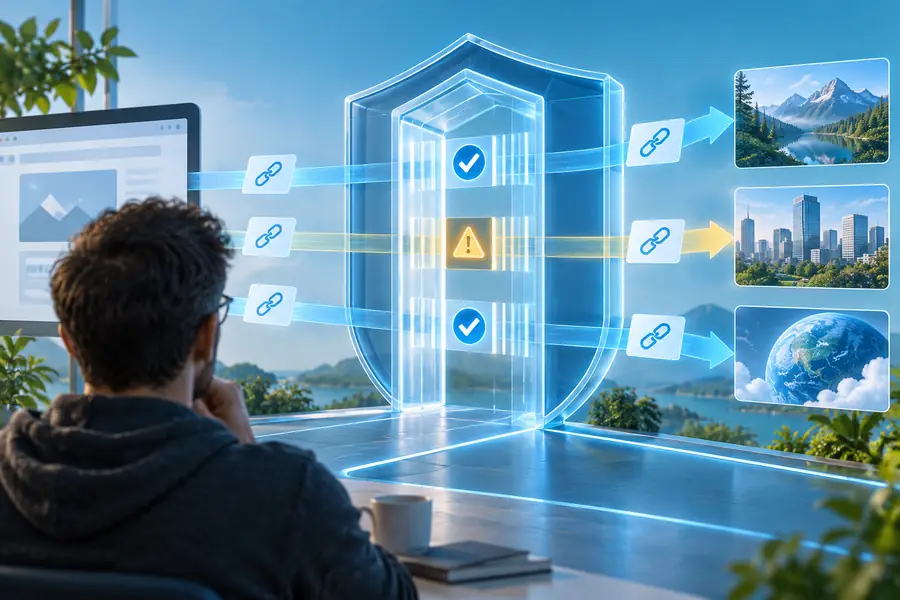
Use public URLs and verify unusual results manually.
Unfiltered submissionSanitized public checkPractical uses
A link checker is a maintenance aid, not a universal answer. These situations call for a safer boundary or a different kind of review.
You need a quick inventory of public pages that return errors or redirect unexpectedly.
Use a public starting URL, then confirm important findings in a browser.
You are reviewing an article and want to catch stale citations before publishing.
Check the article after removing preview parameters and private query strings.
You are diagnosing crawl waste caused by dead destinations across a public site.
Pair link results with server logs or analytics instead of assuming every warning is a security issue.
You need malware detection, vulnerability testing, or inspection of an internal application.
Do not rely on a link checker; use approved security tooling and an authorized test process.
Make a careful check
For ordinary website maintenance, keep the scope public, remove secrets from URLs, and treat unusual results as prompts for verification. A checker can save review time without replacing privacy judgment or security testing.
Safety FAQ
These answers address the concerns people commonly raise when researching whether link-checking tools are safe to use.
Usually, yes. A reputable checker generally requests pages that are already public and reports whether linked destinations respond. Use a service with clear ownership and avoid submitting URLs that contain private information.
A normal web-based checker cannot access local files, saved passwords, or unrelated browser data through a submitted website address. Risk increases if you install an unknown extension or desktop program, so verify the publisher before downloading anything.
Avoid doing so unless the service is approved for that environment and its handling of submitted URLs is understood. Preview links, internal hostnames, and access tokens can reveal information even when the page itself is not publicly indexed.
No. A broken result can come from a missing page, temporary outage, redirect problem, timeout, rate limit, or access rule. Confirm the response manually and use a dedicated security tool if you are investigating threats rather than availability.